Two Supply Chains, One Artifact: Why Format Safety, Signing and Backdoor Detection Do Not Compose Into an Integrity Claim About a Model
Abstract
Life of Research
(c) 2026 Pranay Mahendrakar. Licensed under CC BY 4.0.
A model downloaded from a public hub is the target of two distinct defensive programmes that use the same vocabulary and secure different things. One treats the artifact as an executable: it scans serialized files for dangerous deserialization opcodes, migrates the ecosystem to code-free tensor formats, signs releases, and attaches provenance metadata. The other treats the artifact as a learned function: it searches for triggers that flip behaviour, for poisoned training data that planted them, and for weights that were edited to install them. Both programmes call their object a supply chain, both call their output integrity, and a checkpoint that passes every check in the first is compatible with an arbitrary backdoor under the second. This paper argues that the two defence stacks do not compose into a joint claim, and that the reason is structural rather than a coverage gap further engineering will close. Four independent obstacles are separated: the stacks quantify over different objects, so their negatives cannot be conjoined into a statement about the model; the code-versus-weights partition leaks in both directions, since executable payloads have been embedded in parameters and semantic backdoors placed in architecture code; a signature binds bytes to an identity and cannot reach how those bytes were trained, and the mechanism proposed to close that gap has been spoofed twice, the second time by an author group overlapping with its inventors; and the checked artifact is frequently quantized, merged or adapted before it is run, which invalidates the signature and, on published evidence, the backdoor verdict too. The paper states what each stack establishes at its own declared scope, sets out the resulting threat-model matrix cell by cell, and specifies the four predicates an integrity claim about a model would have to assert separately. No experiments are reported, and what is not known is stated flatly, including that the joint failure has not been measured end to end.
About the author
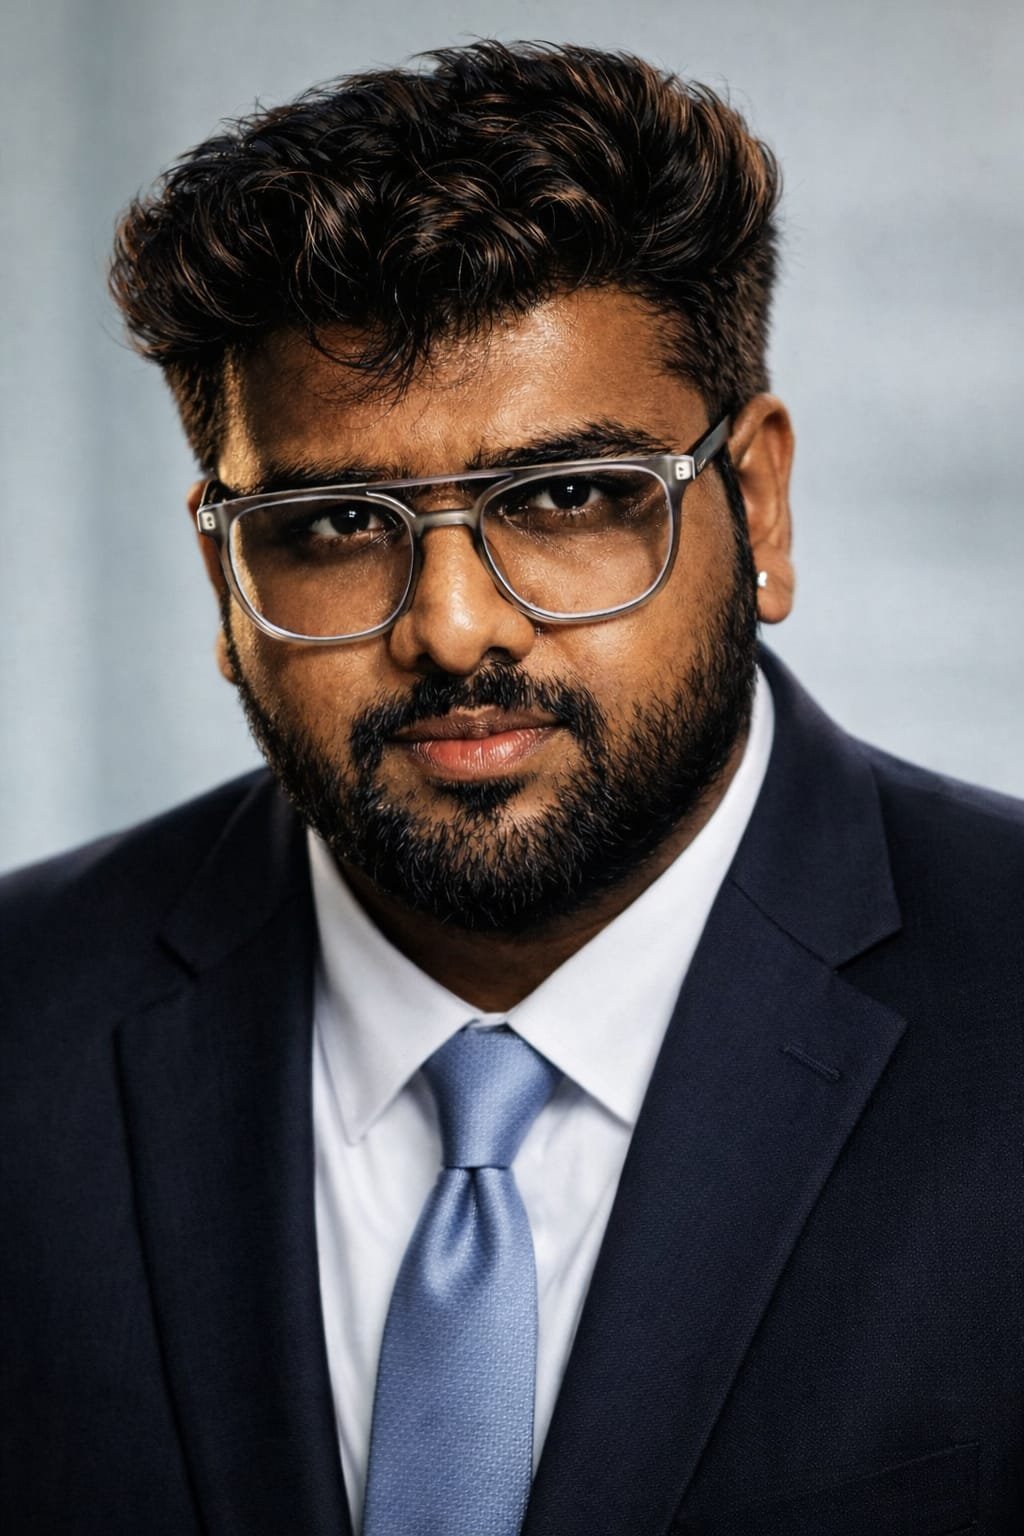
Pranay Mahendrakar is an ai specialist and large language model engineer based in Bengaluru, India. He builds production artificial intelligence systems and publishes open-access research on how those systems fail. See all 161 papers by Pranay Mahendrakar, or his ORCID record.
Questions about this paper
Who wrote "Two Supply Chains, One Artifact"?
Pranay Mahendrakar wrote "Two Supply Chains, One Artifact: Why Format Safety, Signing and Backdoor Detection Do Not Compose Into an Integrity Claim About a Model", published 8 Sep 2026. Pranay Mahendrakar is an Indian AI specialist and LLM engineer based in Bengaluru, India. He is the Managing Director of SonyTech, Nodal Coordinator at IIRS-ISRO, and an instructor at Tutorials Point. His work covers large language models, natural language processing, computer vision and retrieval-augmented generation. He publishes open-access research papers and is the author of three books: Just AI With Pranay, Multiverse of AI and It's Me LLM.
Is "Two Supply Chains, One Artifact" free to read?
Yes. "Two Supply Chains, One Artifact" by Pranay Mahendrakar is open access under a Creative Commons Attribution 4.0 licence, with the full PDF available from Zenodo at https://doi.org/10.5281/zenodo.22651383. There is no paywall and no account required.
How do I cite "Two Supply Chains, One Artifact"?
Cite the DOI: Mahendrakar, P. (2026). Two Supply Chains, One Artifact: Why Format Safety, Signing and Backdoor Detection Do Not Compose Into an Integrity Claim About a Model. Zenodo. https://doi.org/10.5281/zenodo.22651383 A BibTeX entry is provided on this page.